After you install an Edge site or are granted a Collibra Cloud site, you can create a connection to the Azure platform.
Do you use a vault?
|
You can use a vault to add your data source information to your Edge site connection. Check the connection property table below to see which information is available for your vault. Vaults are not available for Collibra Cloud sites. |
No vault
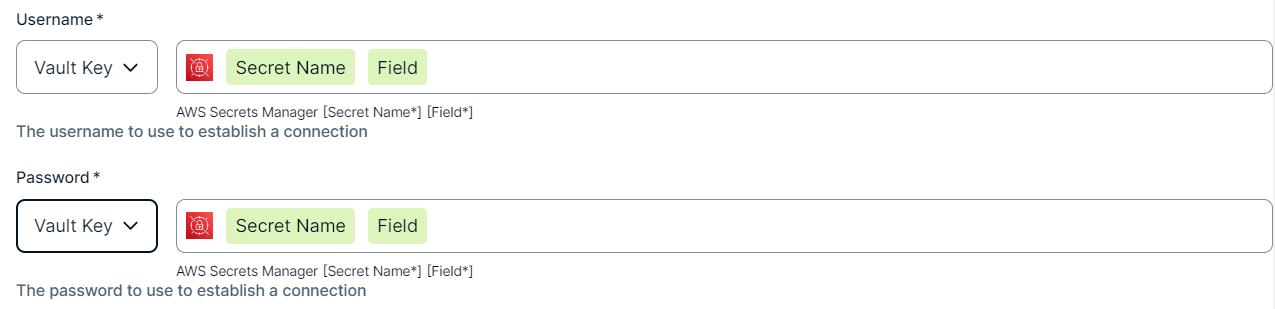
AWS Secrets Manager
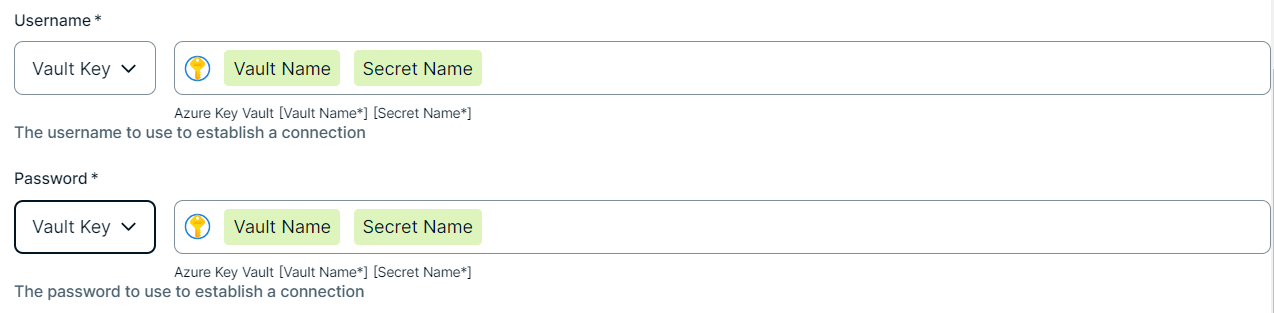
Azure Key Vault
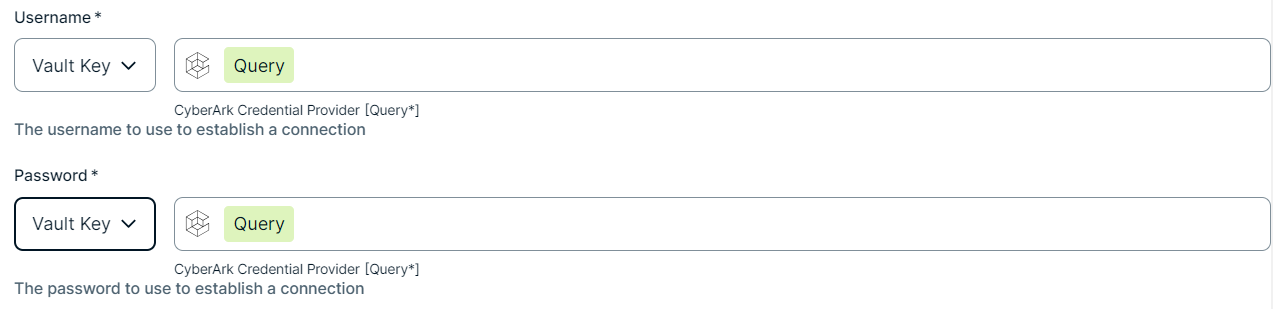
CyberArk Vault
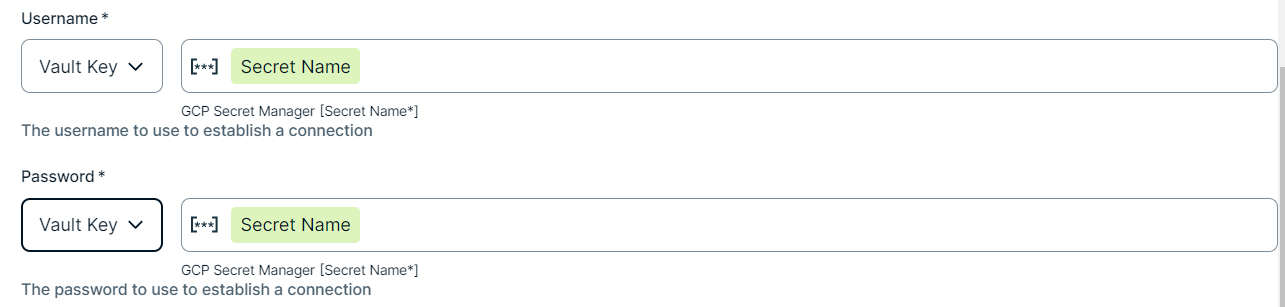
Google Secret Manager
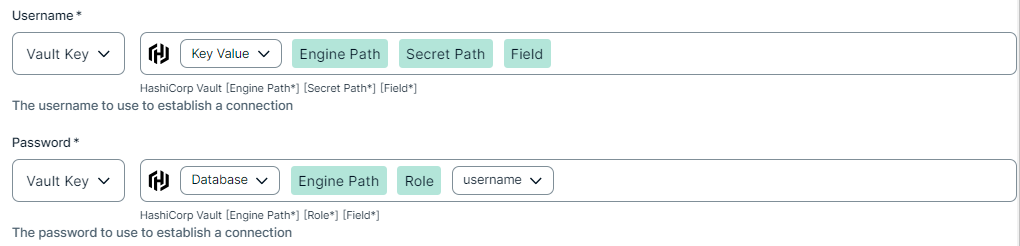
HashiCorp Vault
|
|
|
|
||
|
How to use your vault...
To use your vault, do the following:
To use your vault, do the following:
To use your vault, do the following:
To use your vault, do the following:
To use your vault, do the following:
|
||
Prerequisites
In your Collibra environment
-
You Note
If you have defined an outbound (forward) proxy on your Edge site, the integration will take that configuration into account when connecting to the AI platform. The following proxies are supported, using either a HTTP or HTTPS proxy URL:
- Pass through (No authentication)
- Pass through (Basic authentication)
- No proxy for noProxy hosts defined by Edge
This integration is not supported on Edge sites installed using a Man-in-the-middle (MITM) proxy.
- You have created and installed an Edge site.
- You have added a vault to your Edge site.
- You have a resource role with the Configure external system resource permission, for example, Owner.
- You have a global role with the Catalog global permission, for example, Catalog Author.
- You have a global role with the View Edge connections and capabilities global permission, for example, Edge integration engineer.
In your Azure ML environment
To integrate Azure ML assets, the service principal must have the following permissions on the Azure ML workspace:
Microsoft.MachineLearningServices/workspaces/readMicrosoft.MachineLearningServices/workspaces/models/readMicrosoft.MachineLearningServices/workspaces/models/versions/readMicrosoft.MachineLearningServices/workspaces/metadata/artifacts/readMicrosoft.MachineLearningServices/workspaces/experiments/runs/read
These permissions are included in the built-in AzureML Data Scientist role. The built-in Reader role also includes them and synchronizes all models, including metrics. For more information on role assignments, go to the Azure ML access control documentation. A missing permission can produce a synchronization that shows a status of Completed with models missing and no error reported.
Steps
- Open a site.
-
On the main toolbar, click
 →
 Settings.
The Settings page opens. -
In the tab pane, click Edge.
The Sites tab opens and shows a table with an overview of your sites. - In the table, click the name of the site whose status is Healthy.
The site page opens.
-
On the main toolbar, click
- In the Connections section, click Create connection.
The Create connection page appears. - Select the Azure connection to connect to Azure.
- Enter the required information.
Field Description Required Available for vaults? Name The name of the Edge or Collibra Cloud site connection for Azure.
 Yes
 No
Description The description of the connection.
No
No
Vault The vault where you store your data source values. No
No
Service Principal ID The Application account ID to connect to the Azure.
For information on the Azure Service Principal user and the Application ID, go to the Azure documentation. Yes YesService Principal Secret The application secret for the Service Principal.
For information on the application secret value, go to the Azure documentation. Yes YesTenant ID The Tenant ID of your Azure Active Directory.
For information on the Directory (tenant) ID, go to the Azure documentation. Yes Yes - Click Create.
The connection is added to the Edge or Collibra Cloud site.
You can now add the Azure ML capability to an Edge or Collibra Cloud site.